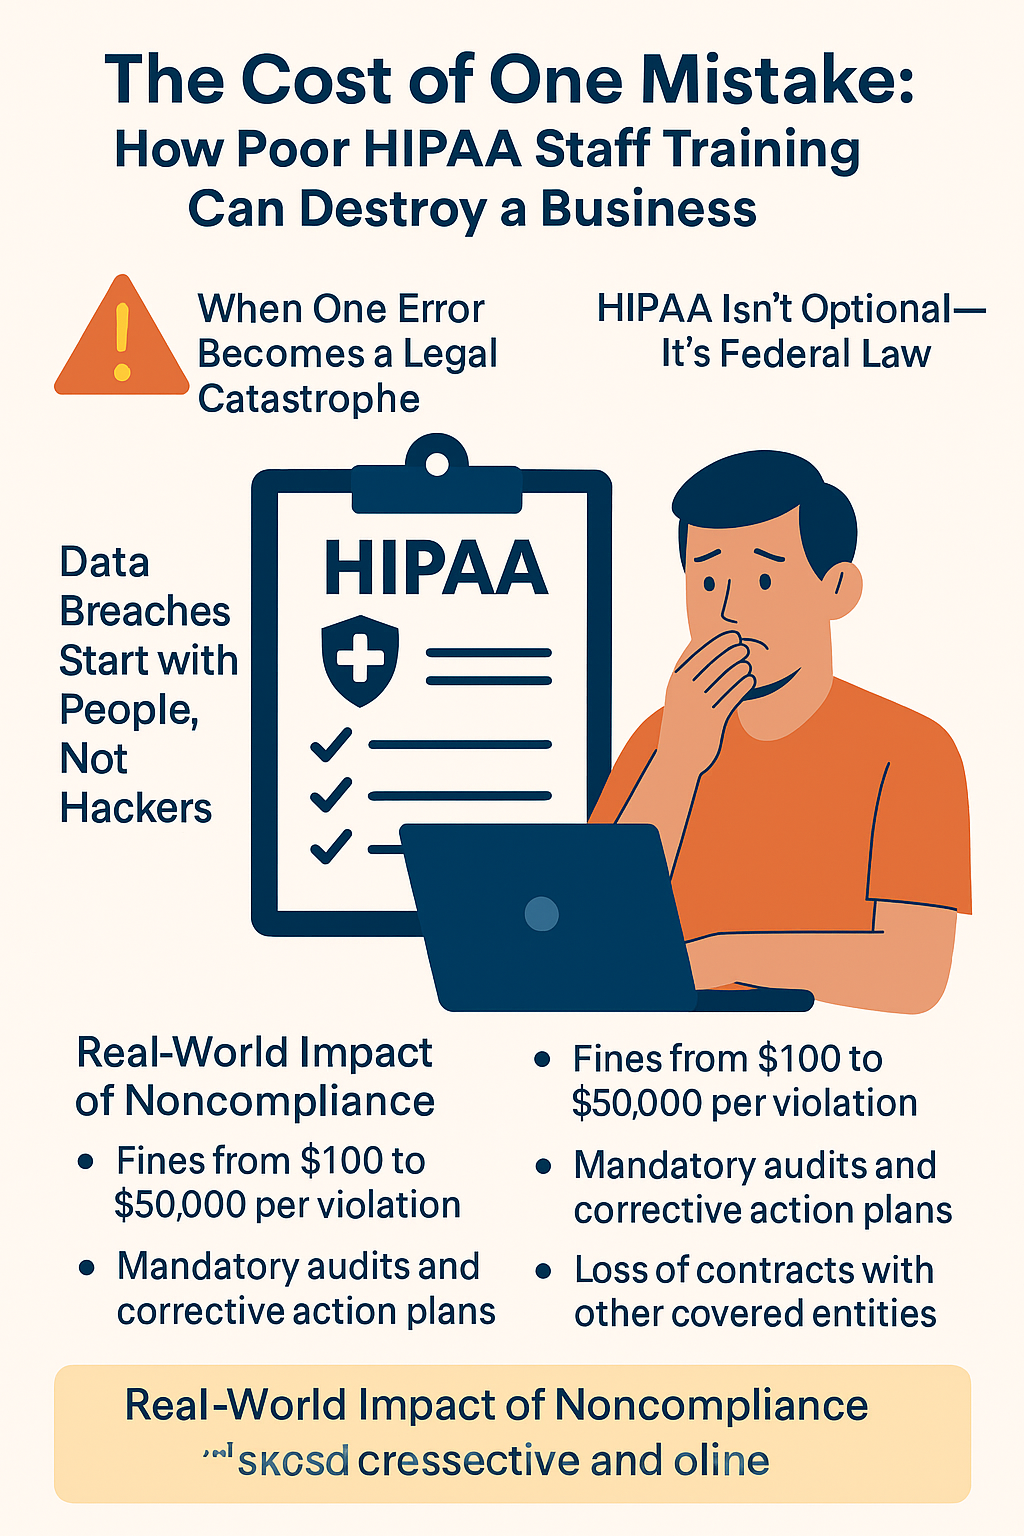
The Cost of One Mistake: How Poor HIPAA Staff Training Can Destroy a Business
When One Error Becomes a Legal Catastrophe
In the modern healthcare industry, a single oversight in handling protected health information (PHI) can lead to devastating consequences. That’s why HIPAA staff training isn’t just a suggestion—it’s a legal necessity. Many healthcare providers and covered entities fail to realize that employees are often the weakest link in maintaining HIPAA compliance. When one untrained staff member mishandles patient information, the result can be a full-blown investigation, public breach notification, and six-figure fines.
HIPAA Isn’t Optional It’s Federal Law
HIPAA stands for the Health Insurance Portability and Accountability Act, and its scope applies to all health care providers, health plans, healthcare clearinghouses, and business associates. It mandates how health information must be handled, stored, and transmitted, especially in electronic form. Failing to comply with HIPAA rules isn’t just risky—it’s punishable by law, with enforcement overseen by the Department of Health and Human Services (HHS).
Data Breaches Start With People, Not Hackers
While many fear outside threats, the truth is that most data breaches in the healthcare industry begin internally. Poor employee training, lack of understanding of security rules, and missing written policies are often to blame. Unencrypted emails, unsecured records, or even a verbal disclosure can lead to violations. HIPAA privacy and HIPAA security rule standards require organizations to mitigate these risks through proactive training.
Real-World Impact of Noncompliance
Violating HIPAA regulations isn’t just a paperwork problem. Businesses have been shut down over exposed medical records, leaked patient data, and failure to notify under breach notification rules. Penalties for noncompliance are steep, including:
- Fines ranging from $100 to $50,000 per violation
- Mandatory audits and corrective action plans
- Loss of contracts with other covered entities
- Civil lawsuits and reputational damage
One business associate who fails to follow HIPAA privacy rule protocols can put your entire operation at risk.
The Role of HIPAA Staff Training
Comprehensive HIPAA training prepares staff to protect private health information and handle it appropriately. That includes understanding:
- How to identify and secure electronic protected health information (ePHI)
- How to properly complete authorization forms
- The scope of security compliance under the HIPAA security rule
- When and how to follow notification rules
Staff must know not only the rules, but how those rules apply in real-life workflows.
Covered Entities Are Held Accountable
Whether you manage a nursing home, clinic, or healthcare organization, the law holds you accountable for how your team handles patient information. Under the HITECH Act and Omnibus Rule, you are responsible for training all employees and ensuring business associate agreements are in place. Simply hiring a third party does not absolve you of responsibility.
Common Violations Linked to Poor Training
When HIPAA privacy training is neglected, mistakes are inevitable. Here are frequent issues that arise:
- Leaving health records in public view
- Accessing patient data without proper authorization
- Faxing medical records to the wrong number
- Disclosing information without consent
- Failing to perform risk assessments or risk analysis
Each of these actions can be avoided with ongoing, role-specific HIPAA staff training.
The HITECH Act Increased Enforcement
The Health Information Technology for Economic and Clinical Health Act (HITECH) was introduced to promote secure use of electronic health records and expand enforcement of HIPAA compliance. It increased penalties, enabled state attorneys general to prosecute violations, and put a spotlight on security rules.
For clients in the healthcare industry, this means one thing: even minor training oversights can result in massive consequences.
HIPAA Staff Training Is More Than a One-Time Requirement
Contrary to what many believe, HIPAA training isn’t a one-and-done exercise. Annual training, updates aligned with policy changes, and scenario-based refreshers are required to ensure true compliance. Proper programs include testing comprehension and documenting participation.
At Masterly Consulting Group, we help healthcare organizations establish recurring training programs built around privacy and security best practices.
Poor HIPAA Training Affects More Than Just Fines
The financial risks of noncompliance are high, but the operational damage is just as devastating. Breaches often lead to:
- Lost patient trust and loyalty
- Public disclosure through HHS breach lists
- Contract termination with payers and healthcare plans
- Disrupted care due to investigation protocols
One small error in managing healthcare information can grind your business to a halt.
State Privacy Laws Add More Complexity
In addition to federal HIPAA rules, many states have their own state privacy laws with even stricter provisions. Without expert-led HIPAA staff training, it becomes easy to overlook these overlapping requirements. Businesses must train their teams to comply with both state and federal regulations.
Every Role Needs Specific Training
Front desk staff, billing clerks, physicians, and business associates all interact with protected health information differently. That’s why HIPAA compliance must be tailored to the duties of each role. Masterly Consulting Group helps clients develop targeted, role-specific training programs that reflect real-world responsibilities.
The Role of Risk Analysis in Preventing Breaches
Conducting a risk analysis is a critical requirement under the security rules. Yet many organizations either skip this step or perform it once and never revisit it. A proper risk analysis helps identify gaps in security, set training priorities, and implement controls. Our team supports you in completing and updating your analysis as regulations and workflows evolve.
What HIPAA-Compliant Training Should Look Like
To be truly HIPAA compliant, training must be:
- Conducted annually (or more frequently)
- Tailored to specific roles and responsibilities
- Focused on both privacy rule and security rule standards
- Inclusive of updates tied to the calendar year or legislative changes
Training should also address threats posed by modern technologies, such as mobile devices, email communication, and cloud-based storage.
Business Associates Are Often the Overlooked Risk
Many covered entities assume their business associates will handle HIPAA compliance themselves. However, if a billing company or contractor violates HIPAA privacy, the covered entity may still be held accountable. That’s why training must extend to reviewing and enforcing business associate agreements.
The Omnibus Rule Made Training Non-Negotiable
The Omnibus Rule of 2013 expanded the obligations of covered entities and business associates, particularly regarding breach notification rules and authorization forms. It emphasized the need for proper HIPAA training and clear documentation of all privacy policies and security protocols. Ignoring these updates can lead to severe violations.
PHI Isn’t Just in Paper Charts Anymore
Today’s protected health information exists in emails, texts, cloud software, and even personal mobile phones. Employees must be trained on how to transmit healthcare information safely across all platforms. This includes understanding when encryption is required and how to secure access to systems storing electronic protected health information.
HIPAA Compliance Affects Everyone
From solo healthcare providers to large healthcare organizations, HIPAA compliance is not just the responsibility of compliance officers or IT staff. It affects front-line employees, administrative personnel, and even volunteers. Every individual must be trained to understand the impact of a HIPAA privacy or security failure.
Masterly Consulting Group’s Approach to HIPAA Staff Training
We bring extensive experience working with clients across the healthcare industry, helping them meet their legal obligations and protect patient privacy. Our specific services include:
- Custom training programs for all staff levels
- Risk analysis and compliance gap assessments
- Updates based on the HITECH Act, HIPAA rules, and state privacy laws
Whether you're a startup practice or a growing network, our team ensures your training aligns with real-world threats and regulatory expectations.
The First Step Toward Protection Is Prevention
Training isn't a luxury—it's your first line of defense against costly, damaging errors. Don't wait for a mistake to trigger an investigation or fine. With the right support, you can prevent breaches, build trust, and stay compliant.
Overlooking the Details: The Risk to Civil Rights, Patient Care, and Health Information Privacy
The Economic Clinical Health Act expanded HIPAA’s reach, tightening enforcement and holding organizations accountable for breaches of personal health information. These include names, phone numbers, diagnoses, and anything linked to a patient’s identity or treatment. Failing to follow strict rules around data handling doesn’t just threaten compliance—it can directly impact patient care and expose your business to civil penalties. Beyond regulatory concerns, mishandling PHI is a civil rights issue, compromising the trust and dignity of patients. Training must cover everything from standard transaction formats to health information privacy to ensure your staff understands what’s at stake in every click, conversation, and printed record.
Your Business Deserves to Be Protected
The truth is, most data breaches are preventable with consistent, well-designed HIPAA staff training. At Masterly Consulting Group, we believe that no healthcare provider should be left guessing about compliance. We’re here to equip your team with the tools and knowledge to protect patient data, preserve your reputation, and avoid legal pitfalls.
Contact us at (888) 209-4055 to book a free consultation. Let’s talk about your training needs, evaluate your current compliance program, and create a tailored plan to safeguard your organization’s future.